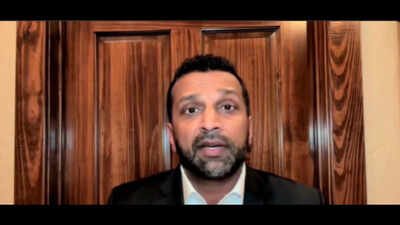
The FBI has engaged more than 750 private-sector companies and arrested over 200 cybercriminals as part of two separate campaigns aimed at protecting American businesses and critical infrastructure from cyberattacks, FBI Director Kash Patel said during a television appearance on Thursday. Speaking to Fox News host Sean Hannity on November 19, Patel discussed the bureau’s Operation Winter SHIELD and Operation Riptide, explaining how the two initiatives were designed to tackle different aspects of the growing cybersecurity threat.While Winter SHIELD focuses on strengthening the digital defences of businesses, government agencies and critical infrastructure, Riptide targets cybercriminals through arrests, extraditions, financial seizures and disruption of their technical infrastructure.Patel’s remarks came amid concerns over a series of technology disruptions affecting banks, airlines, email networks and federal agencies in the US. He said intelligence assessments had found no evidence that foreign adversaries or outside groups were responsible for the reported outages. Patel attributed the disruptions to the rapid replacement of outdated technology and legacy software systems by government agencies and private companies.“There are going to be some technical disruptions like we’ve seen, but the FBI and the intelligence community is going to continuously monitor those activities for nefarious actors,” Patel said.He added that the FBI would hunt down anyone found responsible for malicious cyber activity.
What is Operation Winter SHIELD?
Operation Winter SHIELD, which stands for Securing Homeland Infrastructure by Enhancing Layered Defense, is an FBI cybersecurity initiative designed to help organisations strengthen their protection against hackers and other malicious actors. The bureau launched the 60-day campaign in 2026, bringing together its field offices, private-sector partners and government agencies to improve the security of critical infrastructure.According to Patel, FBI teams have met with more than 750 private-sector companies to establish direct communication channels and encourage businesses to cooperate with federal investigators when cyber intrusions occur.In September testimony before the Senate Judiciary Committee, Patel said all 56 FBI field offices had participated in the campaign, conducting more than 600 engagements across 14 critical infrastructure sectors.The initiative focuses on improving cybersecurity practices, identifying vulnerabilities and ensuring that businesses can respond quickly when their systems are compromised.The FBI has also encouraged companies to adopt 10 defensive measures, including stronger authentication systems, vulnerability management, secure backups, restricted administrator access and regular testing of incident response plans.
Patel compares cyberattacks to hostage situations
During his Fox News appearance, Patel stressed that the first 24 to 48 hours after a cyber intrusion are particularly important. He compared the initial response to a cyberattack to dealing with a hostage situation, saying investigators need immediate access to affected systems to identify attackers and contain the damage.Patel cited an incident last year in which hackers targeted several banks on a Friday afternoon.According to him, the banks quickly cooperated with the FBI, allowing cyber teams to access their systems and remove the attackers by Sunday before any money or customer information was stolen. He said the bureau wanted companies to involve federal investigators early rather than wait until an attack had caused substantial damage.Private companies are not automatically required to give the FBI access to their networks. The initiative therefore relies on voluntary cooperation between businesses and federal authorities.
Operation Riptide: FBI arrests more than 200 cybercriminals
While Winter SHIELD is focused on preventing cyberattacks, Operation Riptide represents the FBI’s offensive approach to tackling cybercrime.The bureau conducted Riptide as a separate 60-day international law enforcement campaign targeting cybercriminal networks that steal money, compromise computer systems and exploit American individuals and businesses.According to Patel, the operation involved 13 coordinated actions with US and international law enforcement partners.In an earlier video outlining the results, the FBI director said the campaign resulted in more than 200 arrests and the freezing or seizure of over $23 million in illicit cryptocurrency and other funds.The FBI also initiated the return of another $31 million in virtual assets stolen by North Korean cybercriminals. Patel said the operation demonstrated how coordinated investigations, financial tracking and international cooperation could disrupt criminal networks operating across borders.He added that cybercriminals could no longer assume that they could escape American law enforcement simply by operating from another country.“Operation Riptide may be over, but we aren’t anywhere close to done,” Patel said in a video released by the FBI. The bureau said its commitment to disrupting cyber threats and pursuing criminals would continue beyond the 60-day campaign.
Patel says FBI has arrested 200 cybercriminals under Trump administration
During his November 19 interview, Patel also highlighted the broader action taken against cybercriminals since the Trump administration took office. He said the FBI had arrested 200 cybercriminals during the administration, including six suspects extradited from overseas.Patel also referred to Operation Blackout, a separate anti-fraud initiative under which federal authorities have seized $17 billion in foreign assets, according to his remarks.
FBI warns Americans about phishing and online scams
Patel said protecting America’s digital infrastructure was not solely the responsibility of federal agencies and large corporations. He urged ordinary Americans to remain alert to phishing attempts, suspicious emails and online scams that could expose personal information or compromise financial accounts. The FBI has encouraged individuals and businesses to report suspicious activity and use its official cybersecurity resources.